CONTENT
Novel evasion techniques through decentralized peer-to-peer architecture
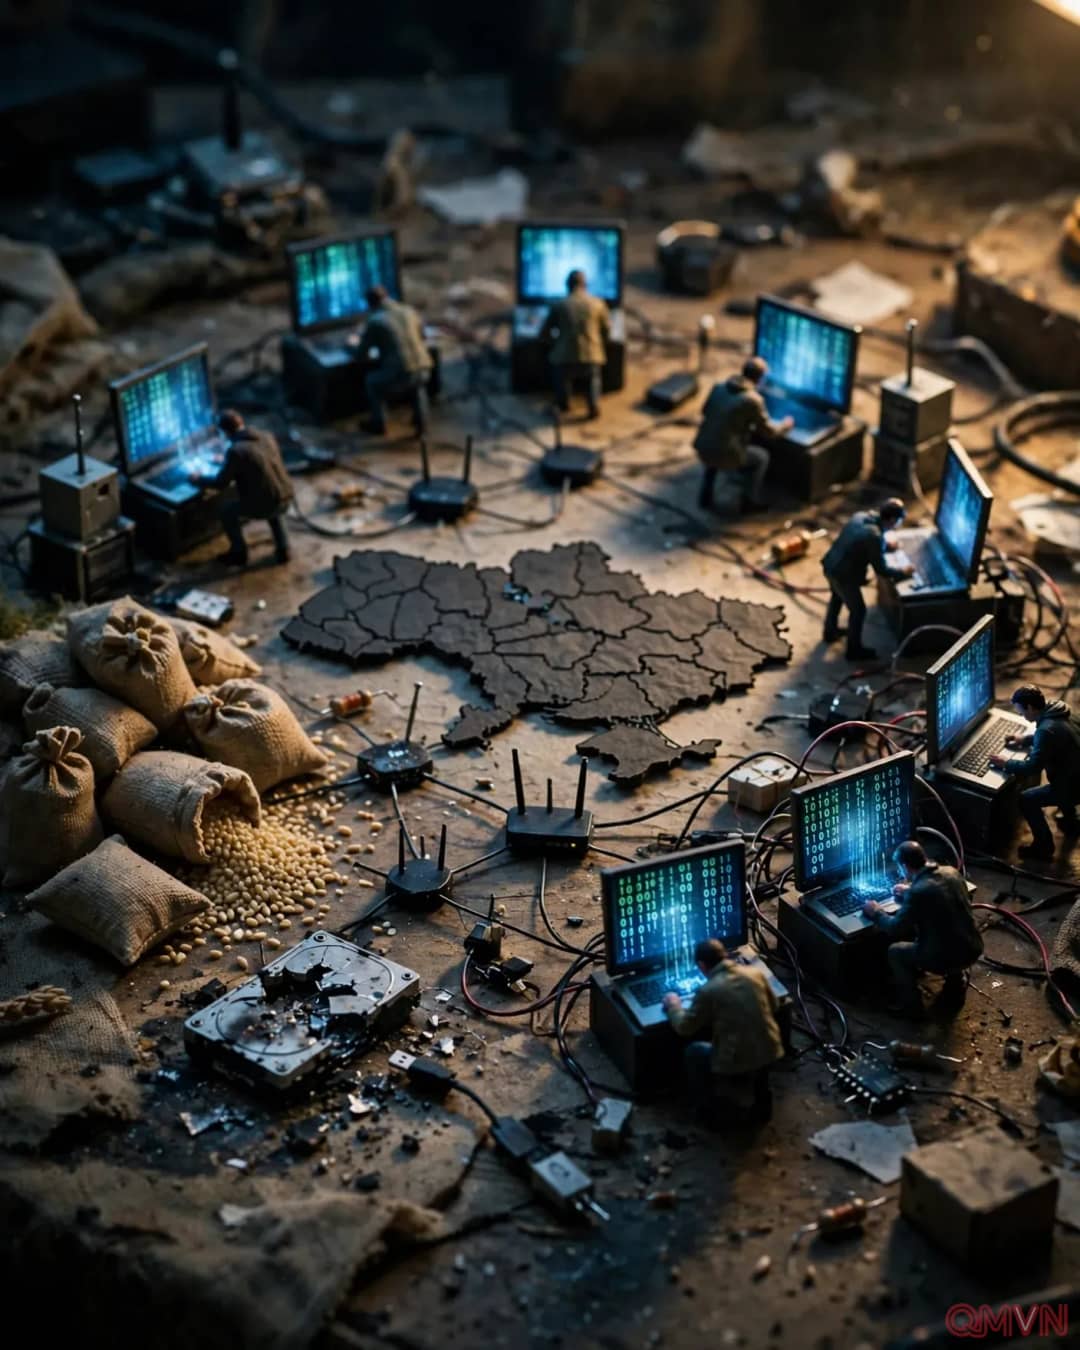
In a comprehensive forensic report published on Thursday, cybersecurity firm ESET revealed that the cyberattack began in July 2025 when operators gained entry into the Ukrainian grain company's enterprise network via a targeted phishing email bearing a weaponized attachment. Once inside, the threat actors deployed specialized software granting unrestricted remote administrative control, enabling them to harvest confidential files, monitor user screens, and exfiltrate proprietary logistics documentation.