Regulatory alerts and architectural scrutiny over application interfaces
The central bank targets software vulnerabilities linking banks and fintechs
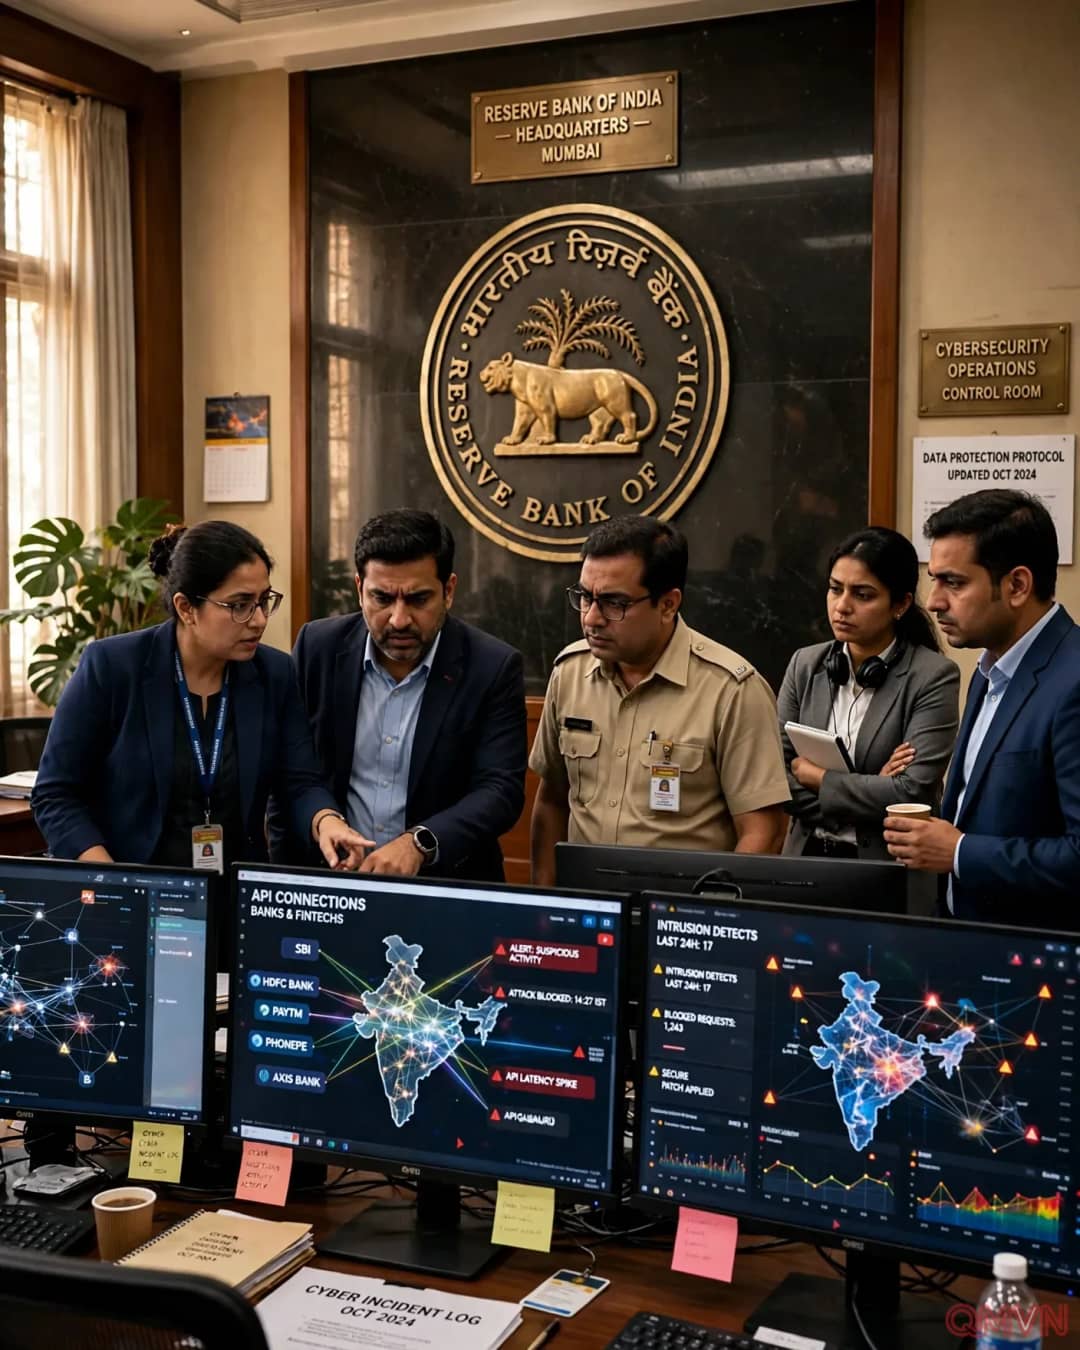
Responding to an unprecedented surge in automated cyber intrusions, the Reserve Bank of India held a succession of confidential meetings with executive leadership across commercial lending institutions. The monetary regulator demanded concrete verification of adherence to existing operational protocols and sought detailed evaluations concerning institutional exposure to malicious artificial intelligence technologies capable of undermining capital reserves and depositor trust.
Regulatory scrutiny centered squarely upon vulnerabilities embedded within application programming interfaces (APIs) — the foundational software connectors banks utilize to facilitate transactional flows with fintech partners and non-banking financial entities.