Sophisticated cyber intrusion penetrating core brokerage networks
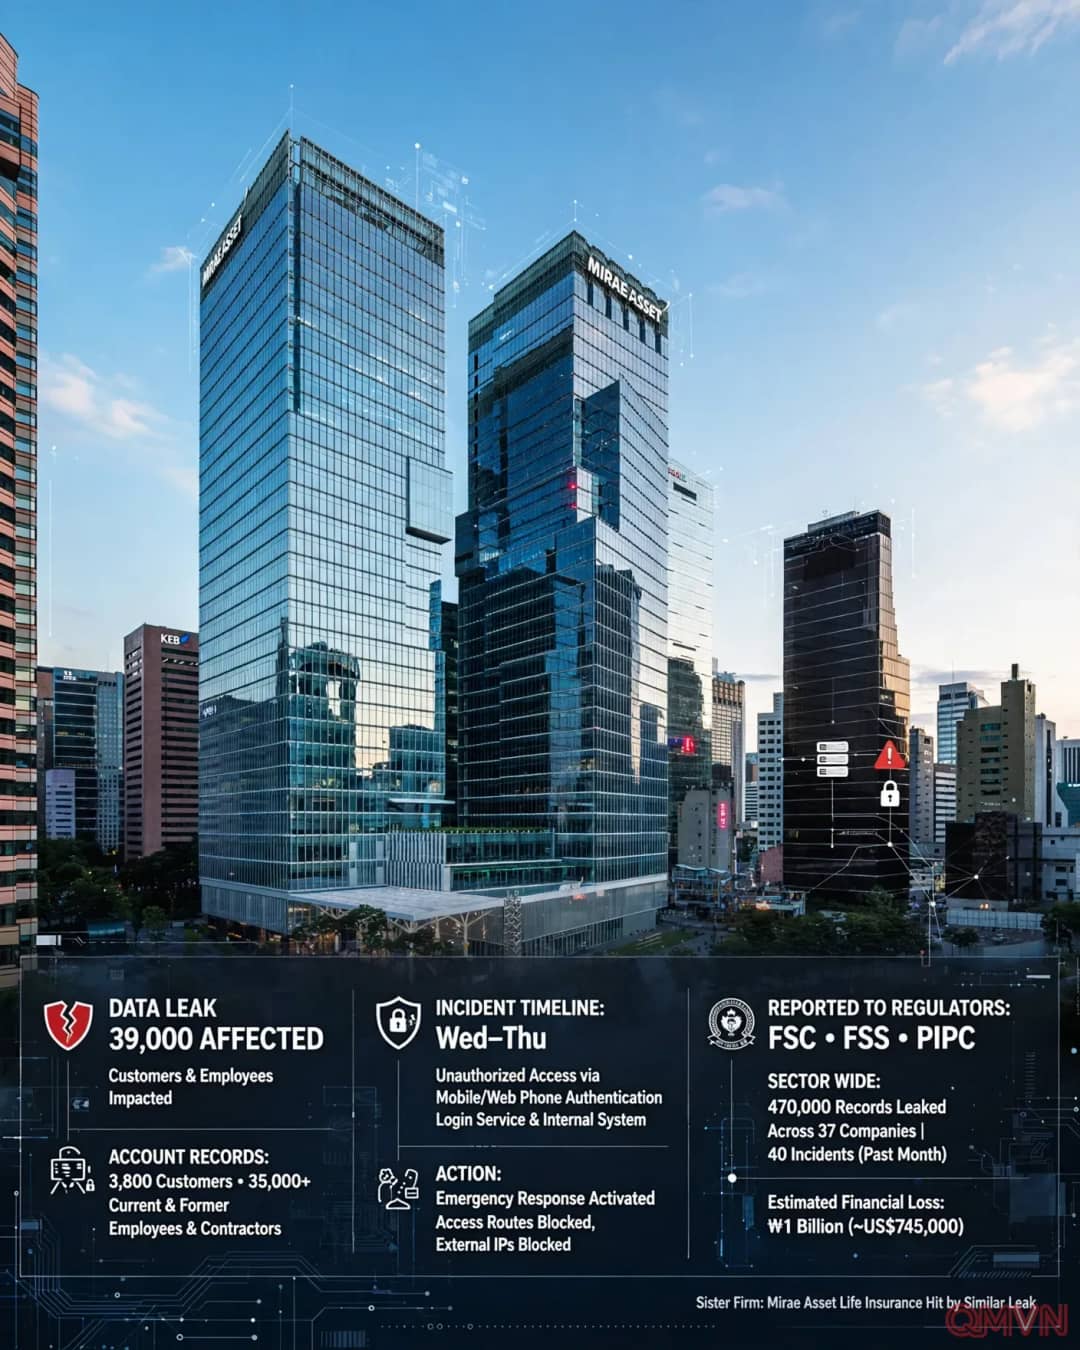
The cyber emergency unfolded when security monitoring teams detected anomalous external IP addresses breaching the company mobile web phone authentication service and subsequently accessing corporate back-end servers. The coordinated cyber offensive occurred over consecutive mid-week days, exploiting authentication interfaces to siphon confidential operational files.
According to the formal corporate disclosure, unauthorized external actors captured the investment account numbers of some 3,800 individual clients, together with full personnel files belonging to more than 35,000 current employees, former staff, and contracted partners. Compromised enterprise fields encompassed full employee names, personnel identification numbers, registered email addresses, personal telephone contacts, and encrypted login passwords.
We immediately blocked the compromised access routes upon identifying anomalous external IP activity and initiated our comprehensive emergency containment protocols.
Unauthorized cyber infiltration breached records belonging to 3,800 investor accounts and 35,000 corporate staff.