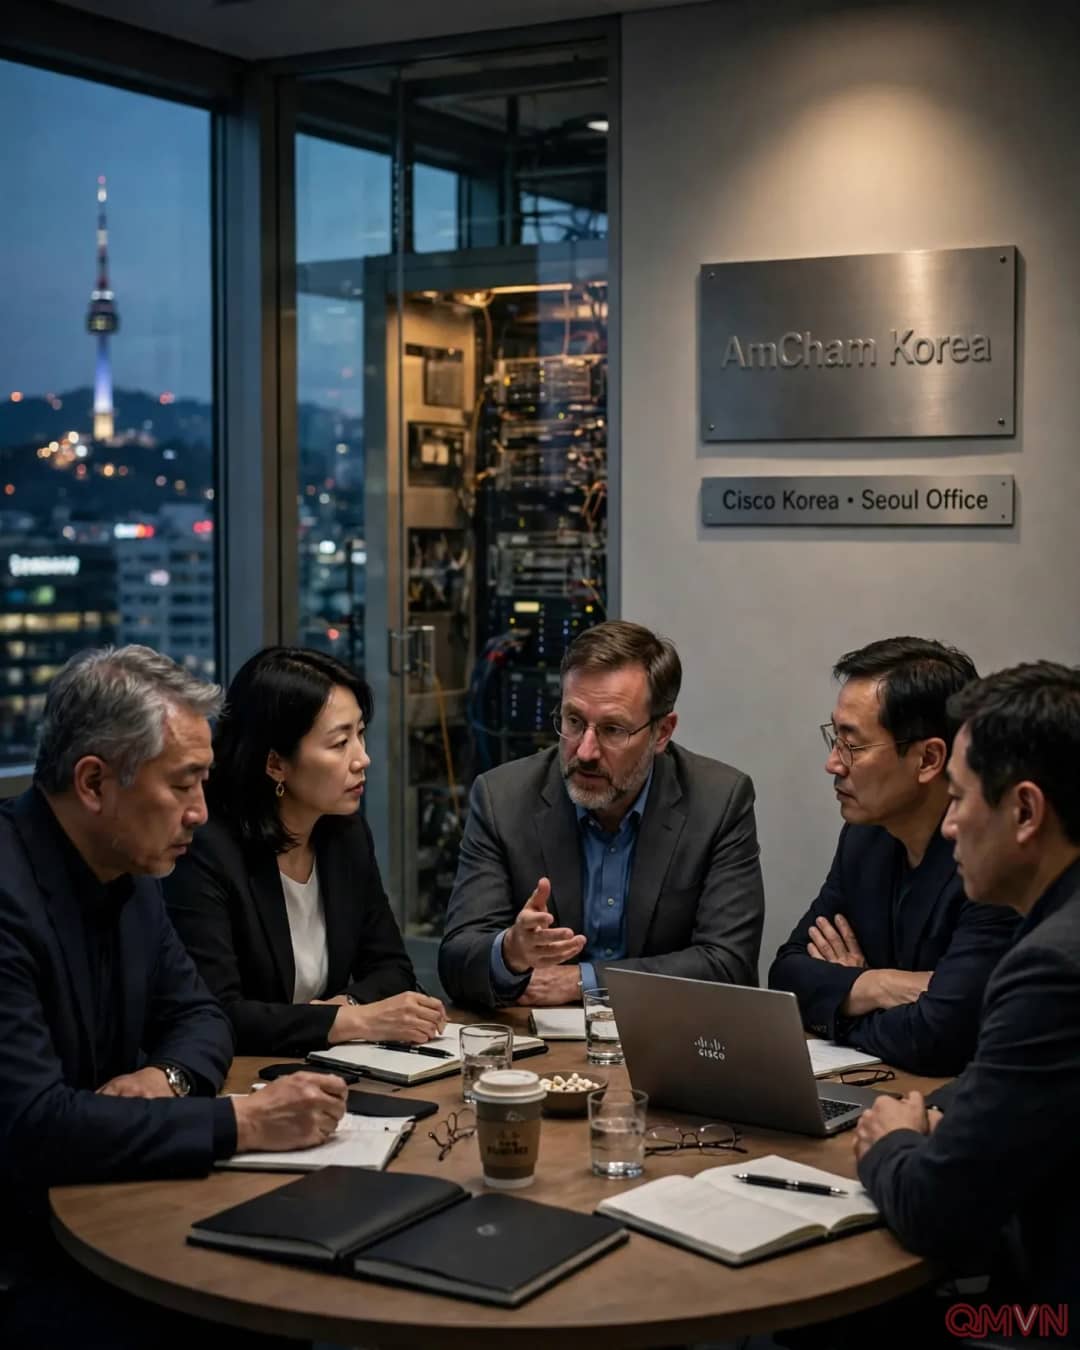
A hidden danger in the server room
In many companies, routers, servers and operating systems keep running smoothly for years, so long that nobody thinks of replacing them. But once a manufacturer stops issuing security patches, that “still working fine” equipment can become the weakest link of all. That was the central message of the roundtable hosted by AmCham Korea and Cisco in Seoul on Thursday.
Speakers argued that AI has changed the rules. When attackers can use automated tools to scan for and exploit vulnerabilities at scale, a single unpatched legacy device can become an entry point into a corporate network, threatening business operations and even critical infrastructure.
From break-fix to long-term strategy
Cisco Korea President Choi Ji-hee stressed that companies should first identify their vulnerable assets, then draw up phased replacement plans based on operational priorities and available budgets, rather than swapping out equipment only after something goes wrong.
“As businesses transition into the AI era, leaving EOL equipment in place after official security updates and technical support have ended can pose a critical threat to business continuity.” – Choi Ji-hee