MAIN STORY
Investigators uncover ARTEX in attack infrastructure
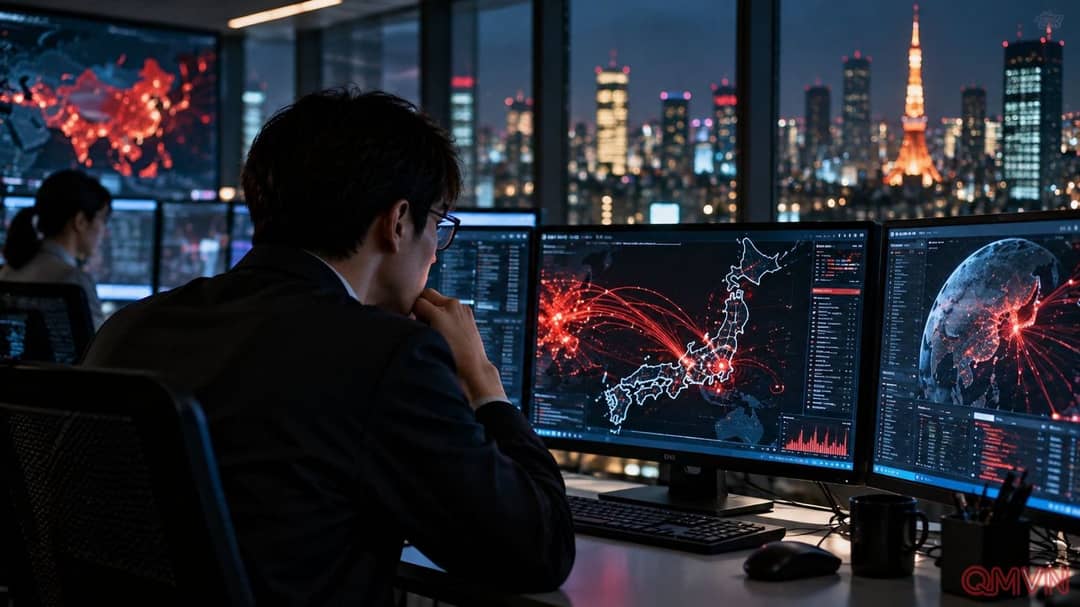
GMO Cybersecurity by Ierae said on October 19 that its examination of infrastructure linked to unauthorized access against Japanese organizations confirmed the presence of ARTEX. Earlier forensic logs had pointed to likely AI involvement; examining the underlying infrastructure strengthened that assessment.
Japanese reports summarizing the inquiry described six AI-enabled attack infrastructures focused largely on companies in Japan. One investigated setup targeted roughly 20 organizations, nine of them in the same industry. Eight companies among identified targets had announced data-leak incidents during September or October. These figures must be distinguished: being targeted, disclosing a breach and having a particular operation conclusively attributed are not the same thing.
A defensive tool can be misused
ARTEX is designed for penetration testing, linking large language models with security utilities to identify potential weaknesses. In an authorized assessment, these capabilities can help defenders locate flaws before criminals exploit them.