The question regulators will ask
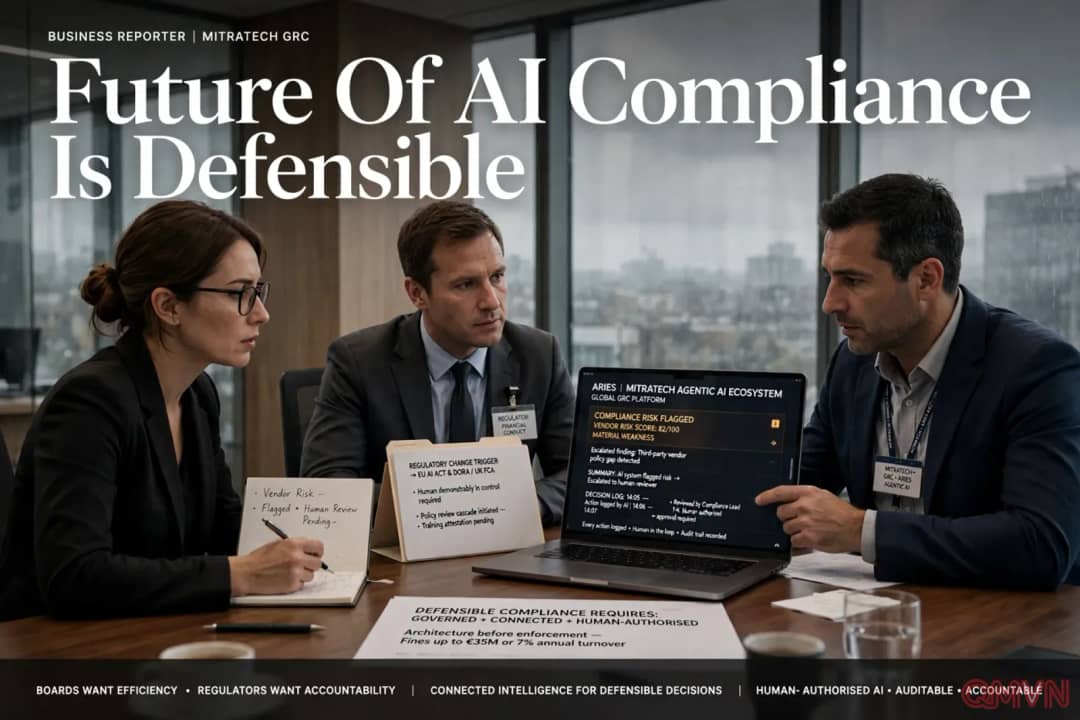
Imagine an AI system has just flagged a compliance risk: it has scored a vendor, escalated a finding and produced a summary. When a regulator walks in, they will not ask whether the conclusion was correct but how the company reached it, who reviewed the output, what record exists of that review, and whether the person who acted on it had the authority and context to do so.
AI identifying an issue on its own is not a defensible answer. According to the analysis, most compliance teams now use AI, but far fewer have built the architecture to ensure that every AI-supported decision will hold up under scrutiny.
“The question was never whether the AI was right. It was whether you could verify it.” — Mitratech GRC
Pulled in two directions
The EU AI Act does not simply ask whether an organisation uses AI; it asks whether the people deploying it are demonstrably in control. Alongside that runs another pressure: regulatory volume has grown so large that manual processes can no longer cope, pushing companies to use AI.